
Key Revocation
Sometimes a key can no longer be trusted. It may be lost, stolen, or just no longer in use. Then you need a way to tell other people to stop using it.
A revocation certificate does this. It is a small file that marks one key as revoked. A revoked key is no longer valid. Anyone who gets the revoked key, from you or from a key server, can see that they should not use it any more.
Anyone who holds the certificate can revoke the key with it, so keep the file safe.
When to Revoke a Key
Section titled “When to Revoke a Key”- The key was stolen or copied. Someone else may have your private key.
- The key is lost. You cannot get at your private key any more.
- You stopped using the key. For example, you moved to a new key.
- A rule asks for it. Your organization may require you to replace keys from time to time.
Make the certificate ahead of time, while you still have the private key. Then you can act quickly when one of these things happens.
Make a Revocation Certificate
Section titled “Make a Revocation Certificate”You need the private key to do this.
There is a shortcut in the KeyPair Management window. Click the key, then do one of these:
- Right-click the key, open Key Operations and choose Generate Revocation Certificate….
- Open the Operations menu at the top and choose Generate Revocation Certificate….
Either one takes you straight to step 3 below.
The longer way goes through the key’s own window:
-
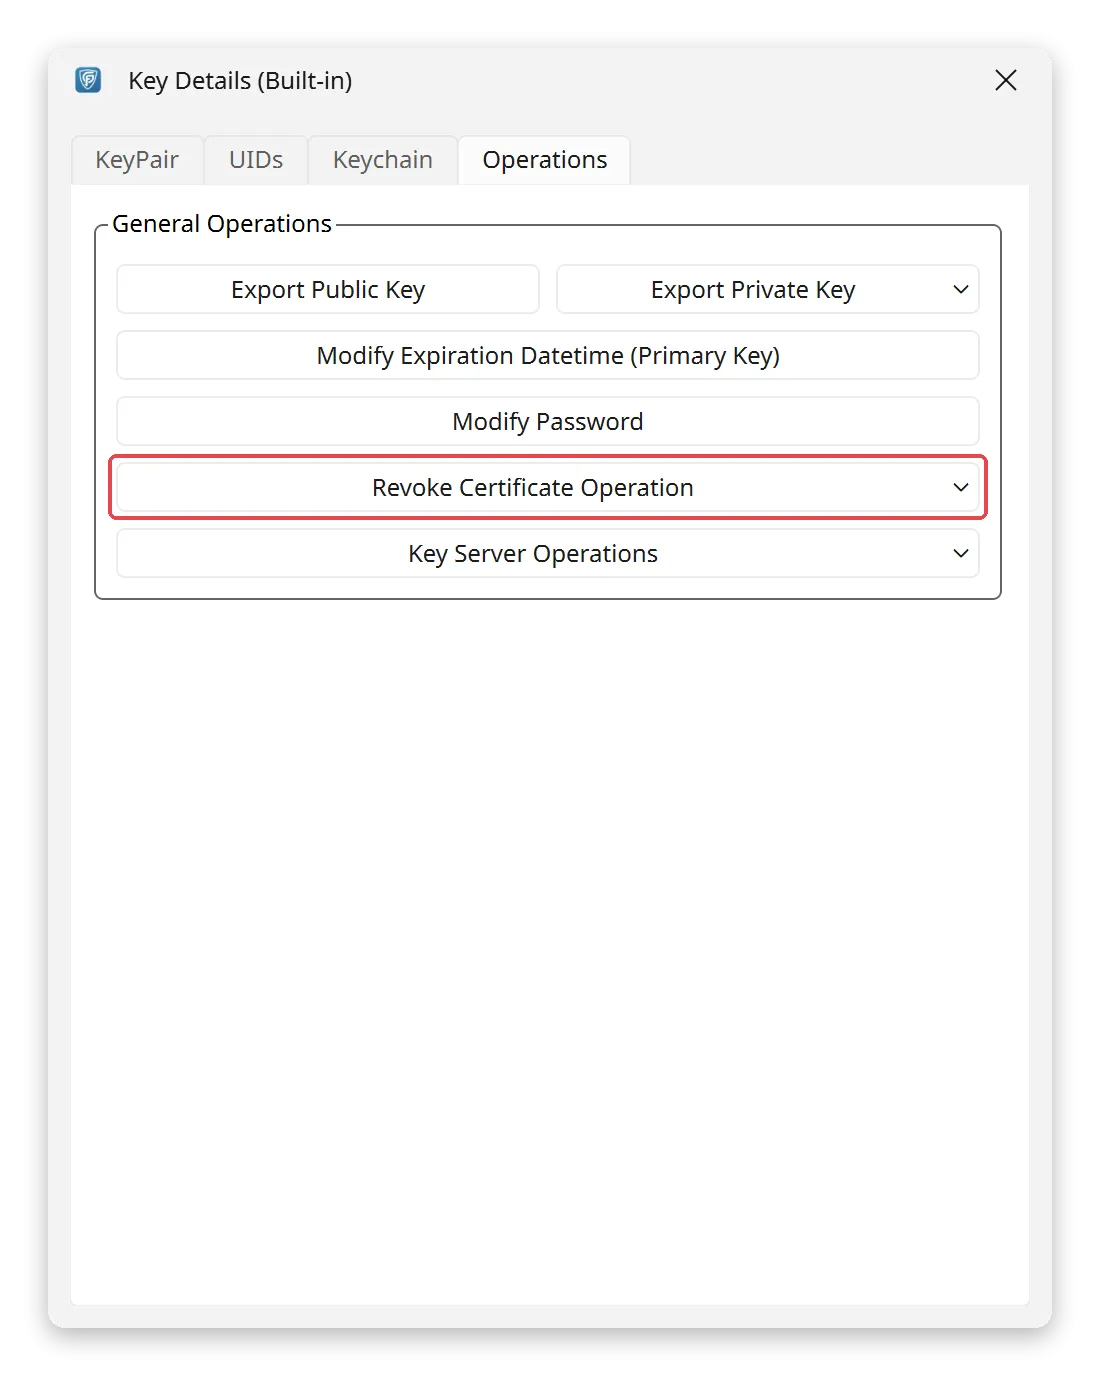
Open the key’s Key Details window and click the Operations tab. See View Key Pair Details for how to open the window.
-
Click Revoke Certificate Operation, then choose Generate Revoke Certificate from the menu. The button is only there for a key whose private primary key you have.
-
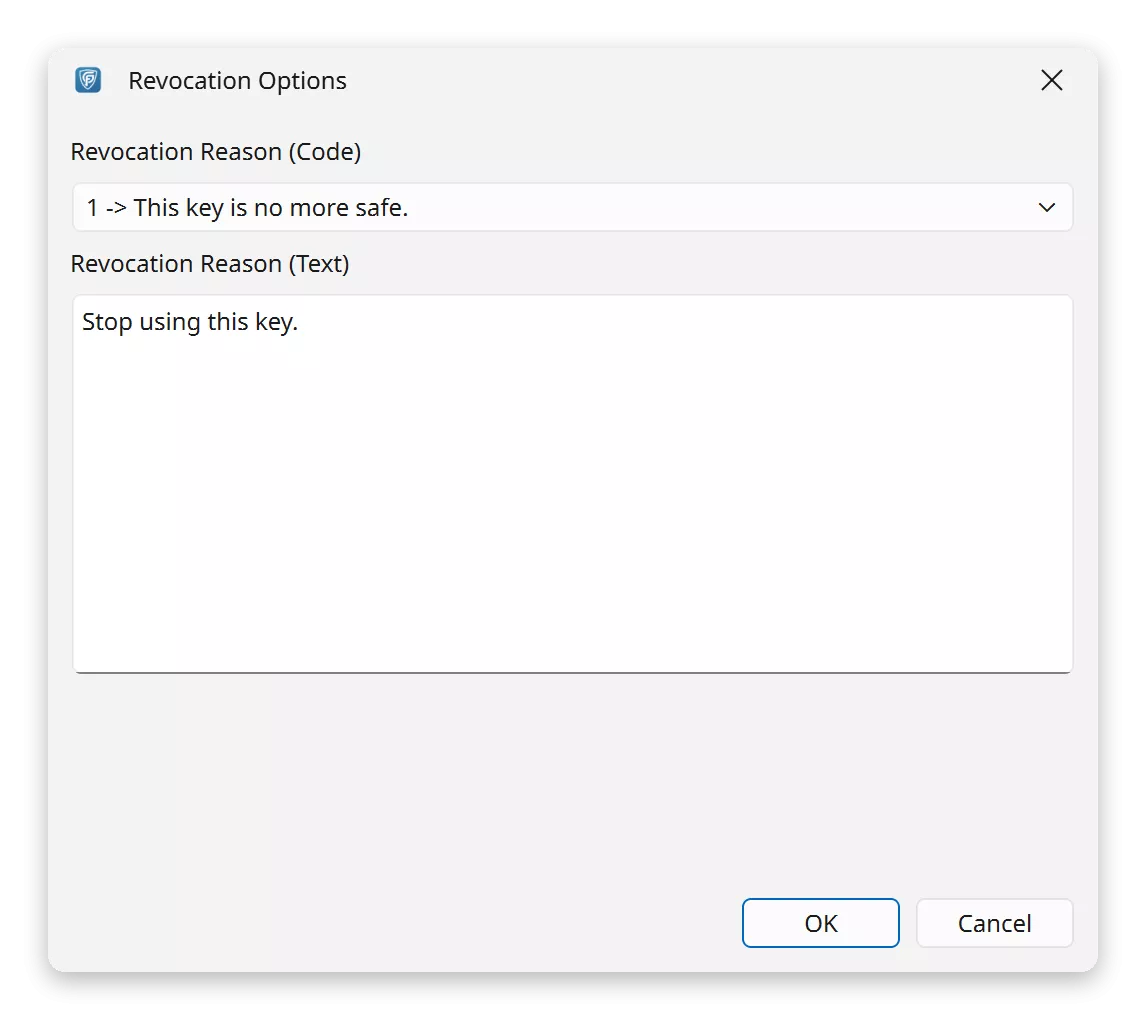
The Revocation Options window opens. Pick a reason under Revocation Reason (Code). If you like, type more details under Revocation Reason (Text). Click OK.
-
Choose where to save the file. Its name ends in
.rev. -
Keep the
.revfile somewhere safe, such as an offline or encrypted drive.
Revoke a Key With a Certificate
Section titled “Revoke a Key With a Certificate”-
Open the key’s Key Details window and click the Operations tab.
-
Click Revoke Certificate Operation, then choose Import Revoke Certificate.
-
A window called Import Key Revocation Certificate asks if you really want to do this. Click OK.
-
Pick the
.revfile you saved earlier and open it. -
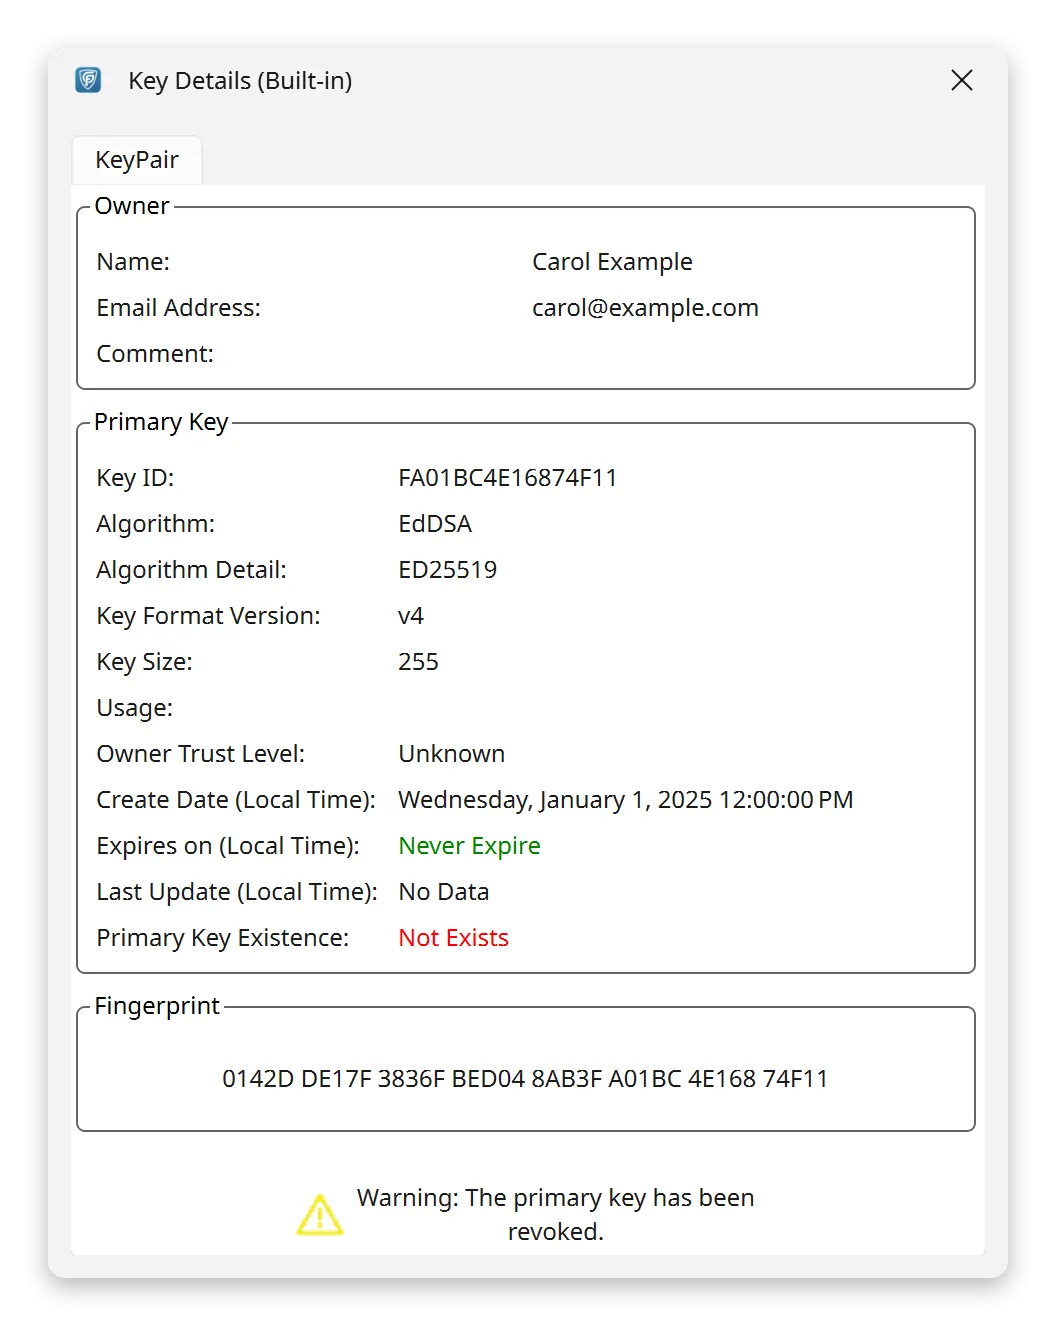
The key is now marked as revoked on this computer.
-
Publish the revoked key to a key server. A revoked key’s details window has only the KeyPair tab, so use the key list instead. Open the KeyPair Management window and click the Revoked category. Then right-click the key and choose Publish Public Key to Key Server.
This menu item comes from the key server module. See Key Server Operations.
You can also publish from the command line:
Terminal window gpg --keyserver hkps://keyserver.ubuntu.com --send-keys <YOUR_KEY_ID>
Good Habits
Section titled “Good Habits”- Prepare early. Make the revocation certificate and back it up before anything goes wrong.
- Store it safely. Keep the
.revfile offline or on an encrypted drive, so nobody else can revoke your key. - Tell people. After you publish the revocation, ask your contacts to refresh your key.