A key server is a place on the internet that stores public keys. Think of it
as a public phone book for keys. You can use it to find, share and update
public keys.
Key servers are handy when:
You want to encrypt a message but you do not have the other person’s public
key.
You want other people to be able to find your public key.
You want the newest copy of a key, for example to see if its owner has revoked
(cancelled) it.
GpgFrontend gives you simple buttons and windows for all of this. You do not
need to type any commands.
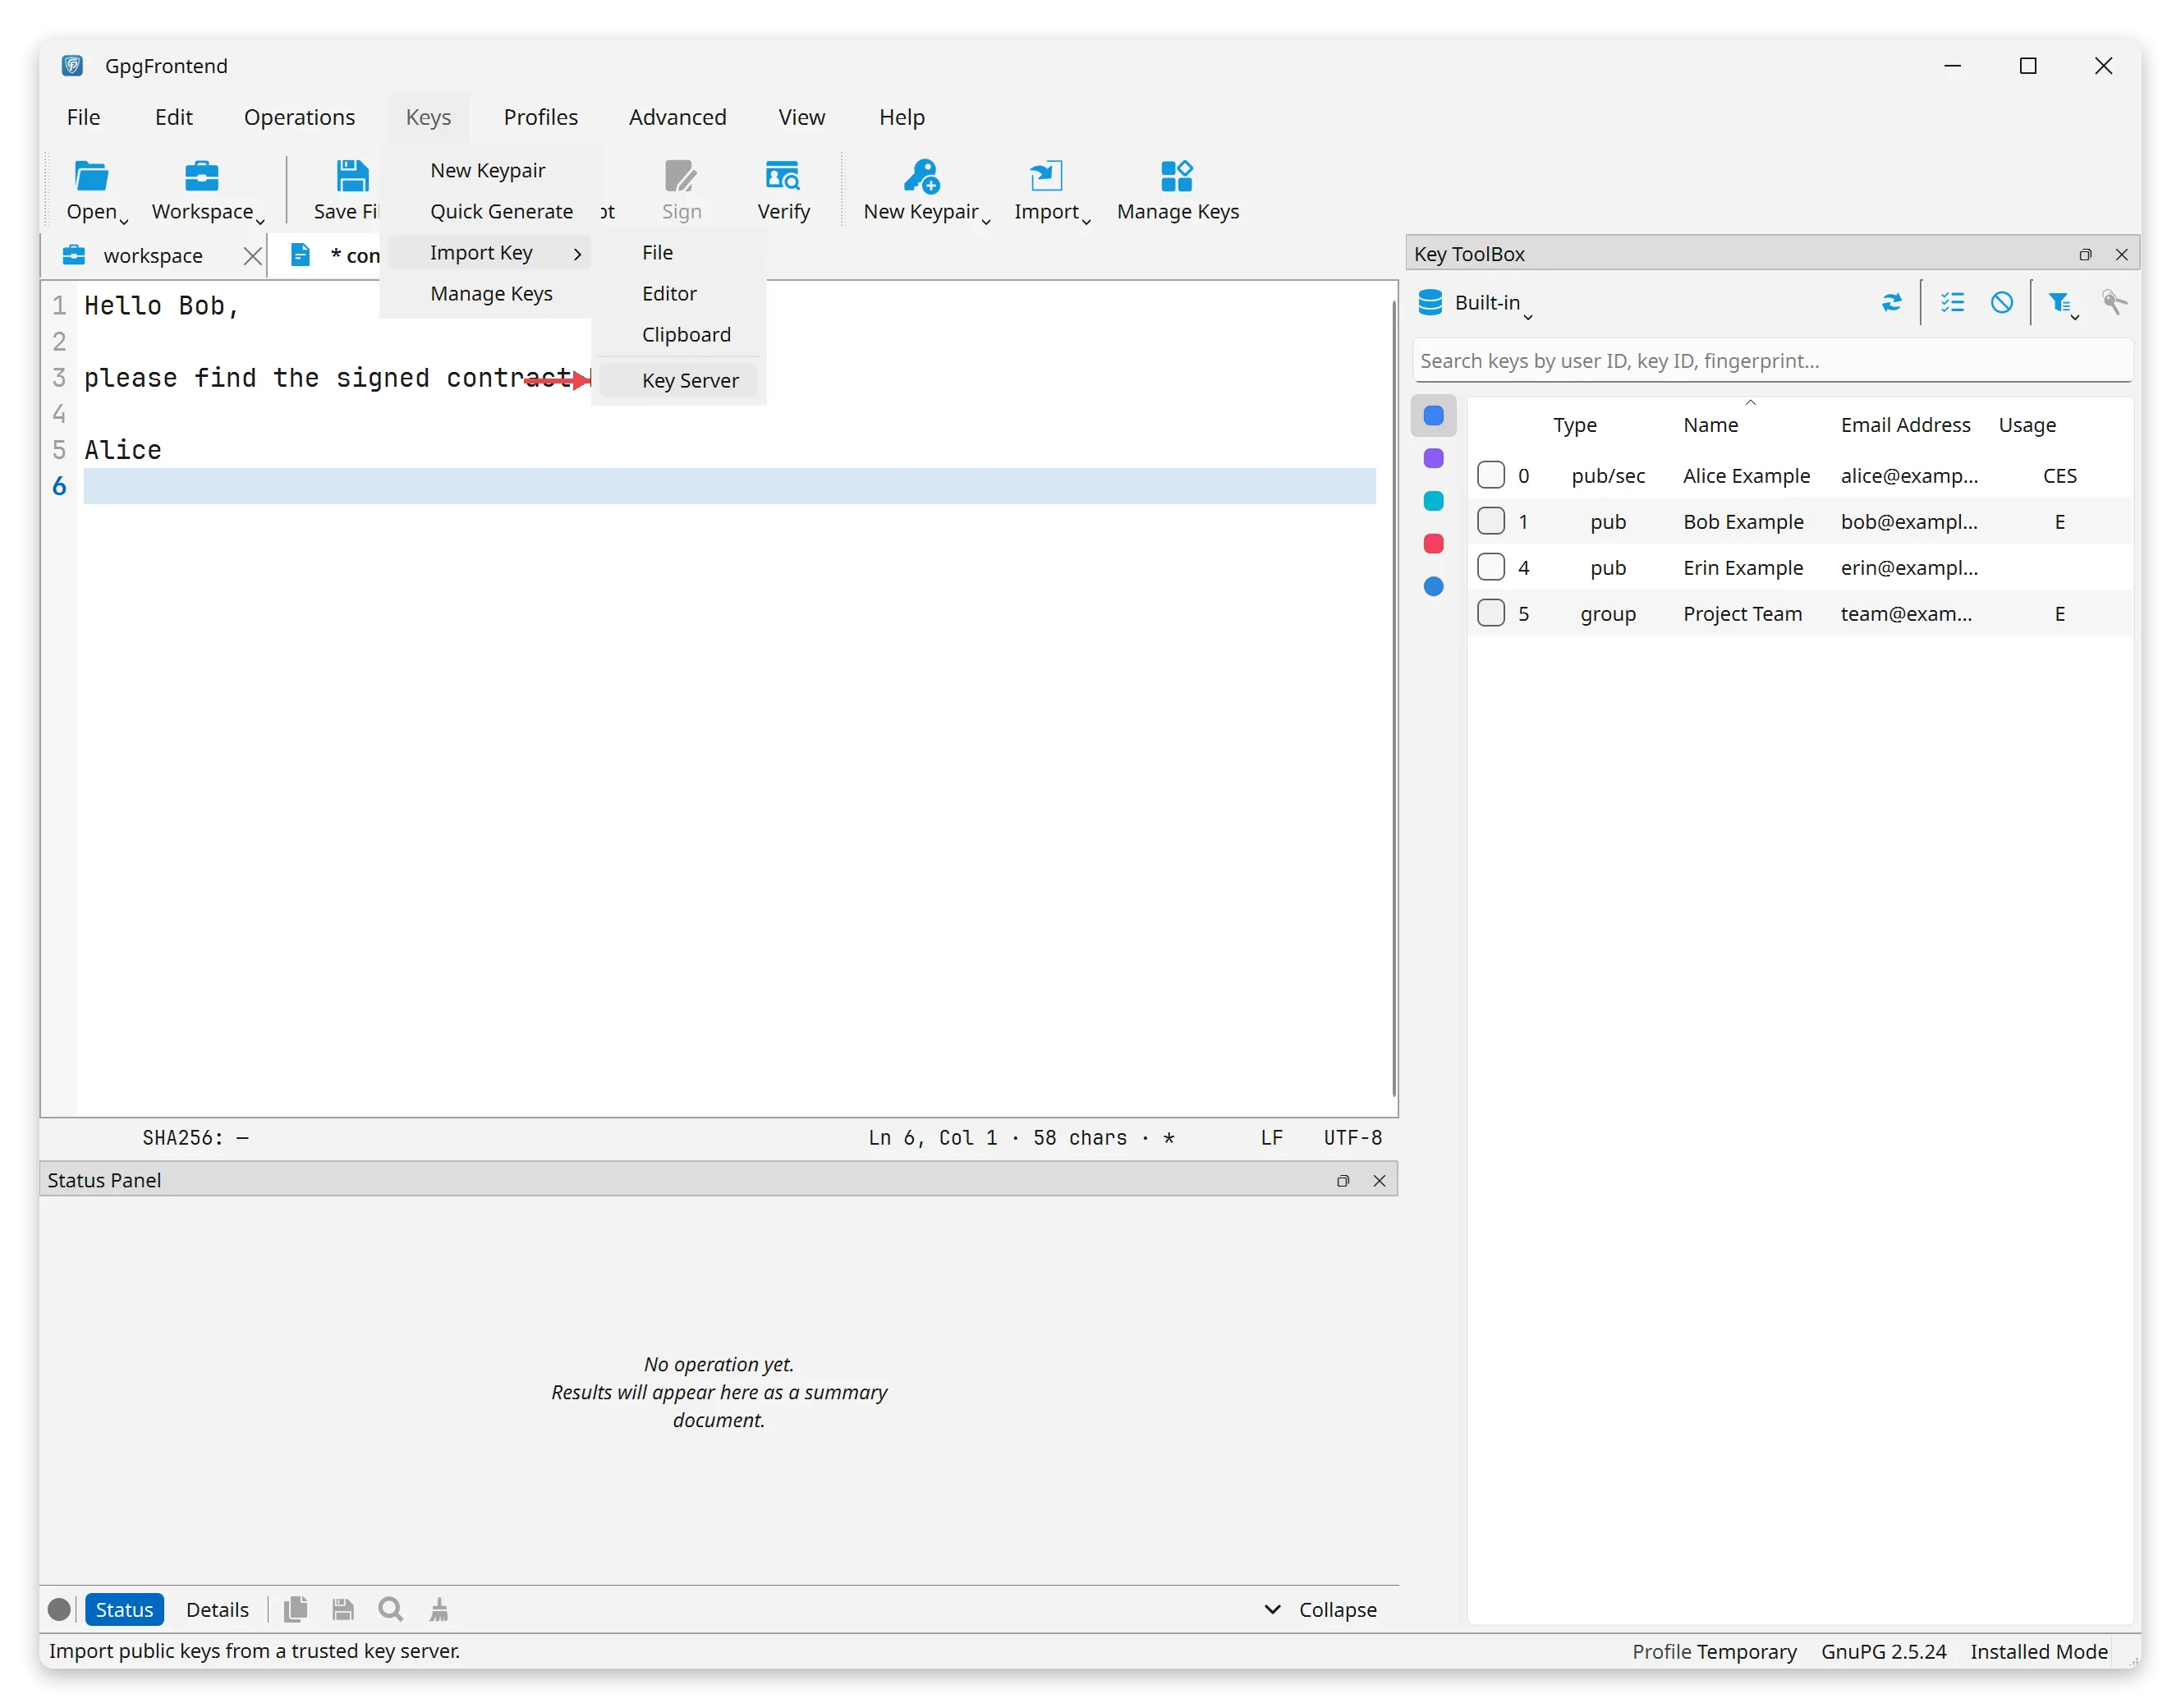
In the main window, click Keys in the menu bar, then Import Key, then
Key Server. You can also click the Import button in the toolbar and
choose Key Server.
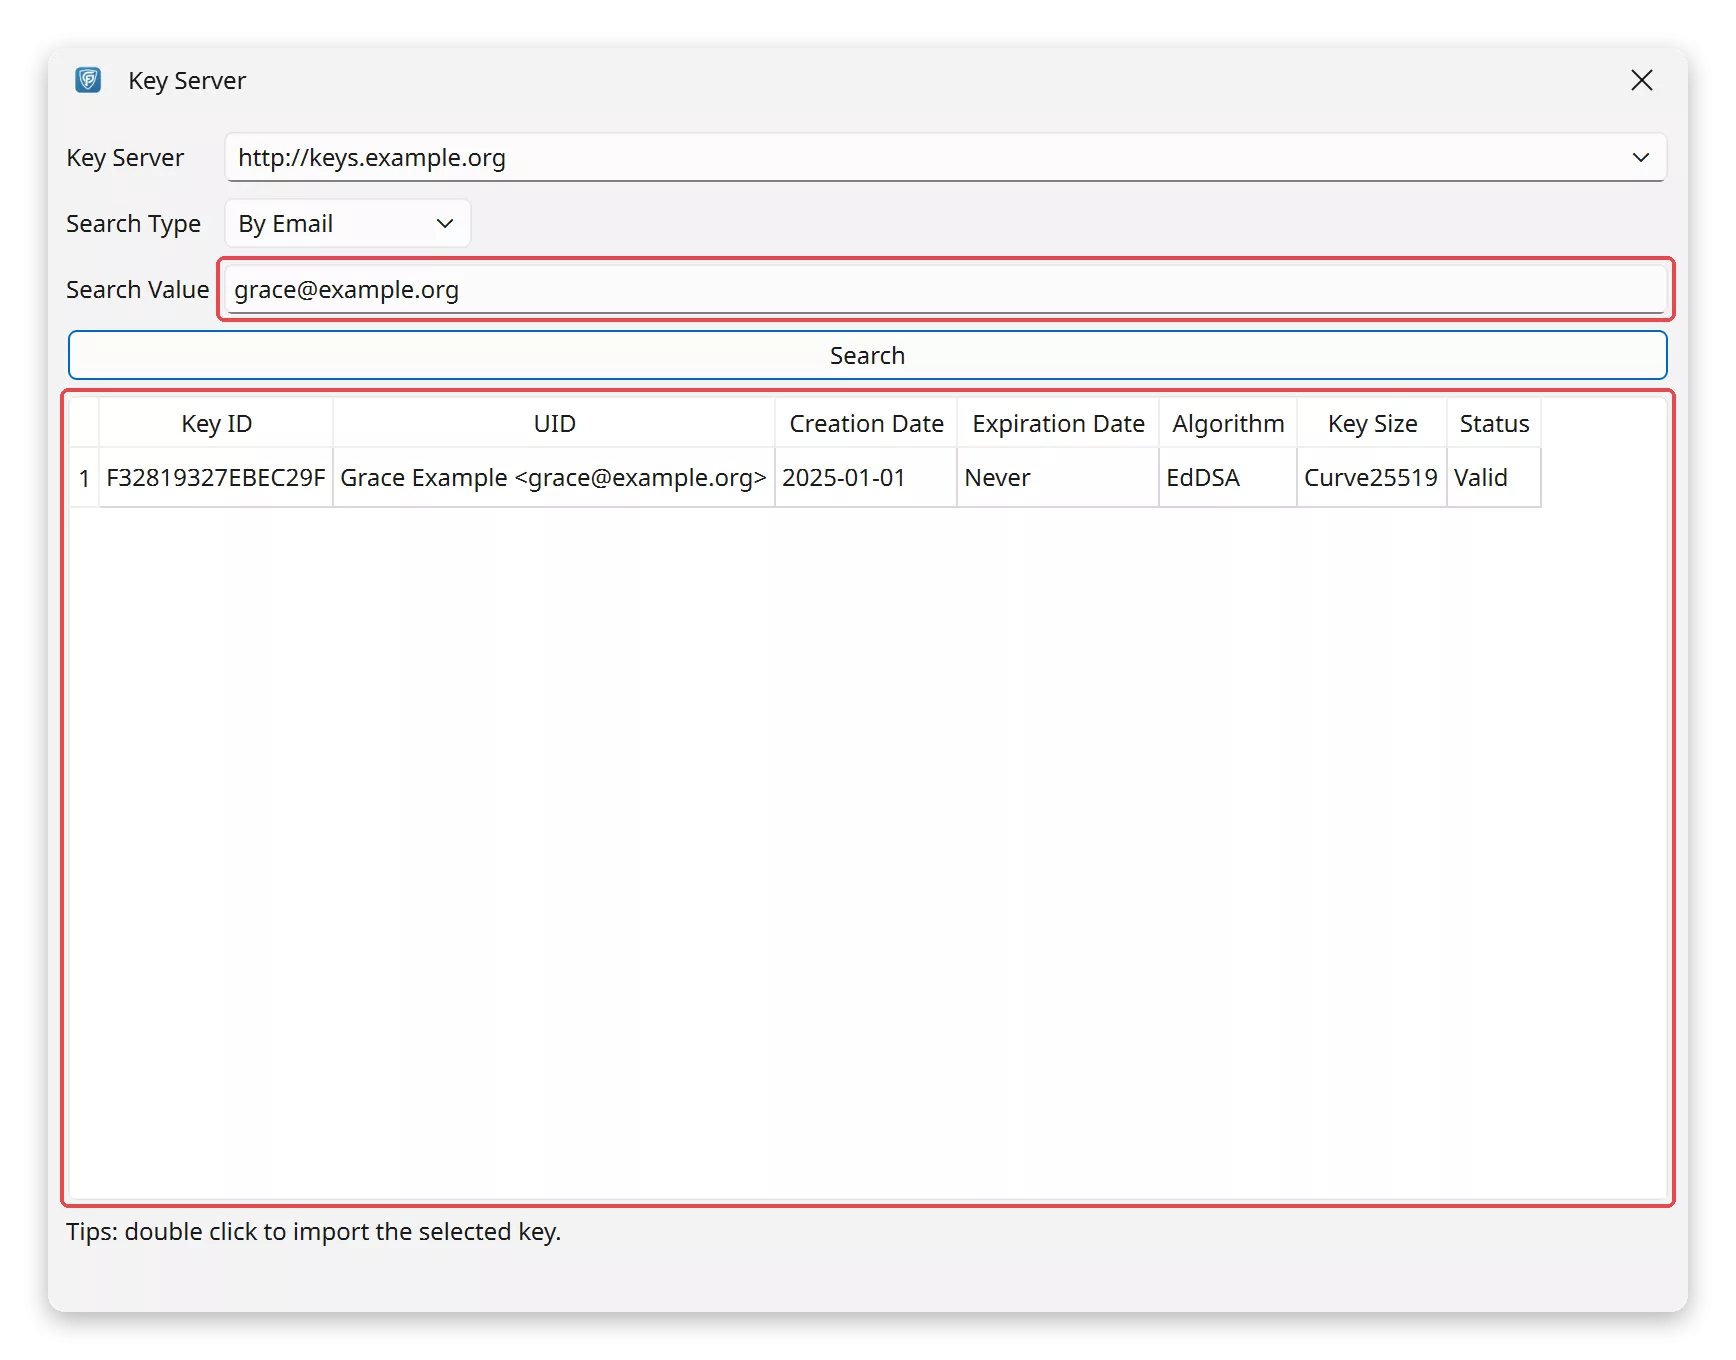
The Search Keys window opens. Under Key Server, choose a server from
the list.
Under Search Type, choose By Key ID, By Email or By
Fingerprint.
Type what you are looking for in the Search Value box.
Click Search, or press Enter. The keys that match appear in
the table.
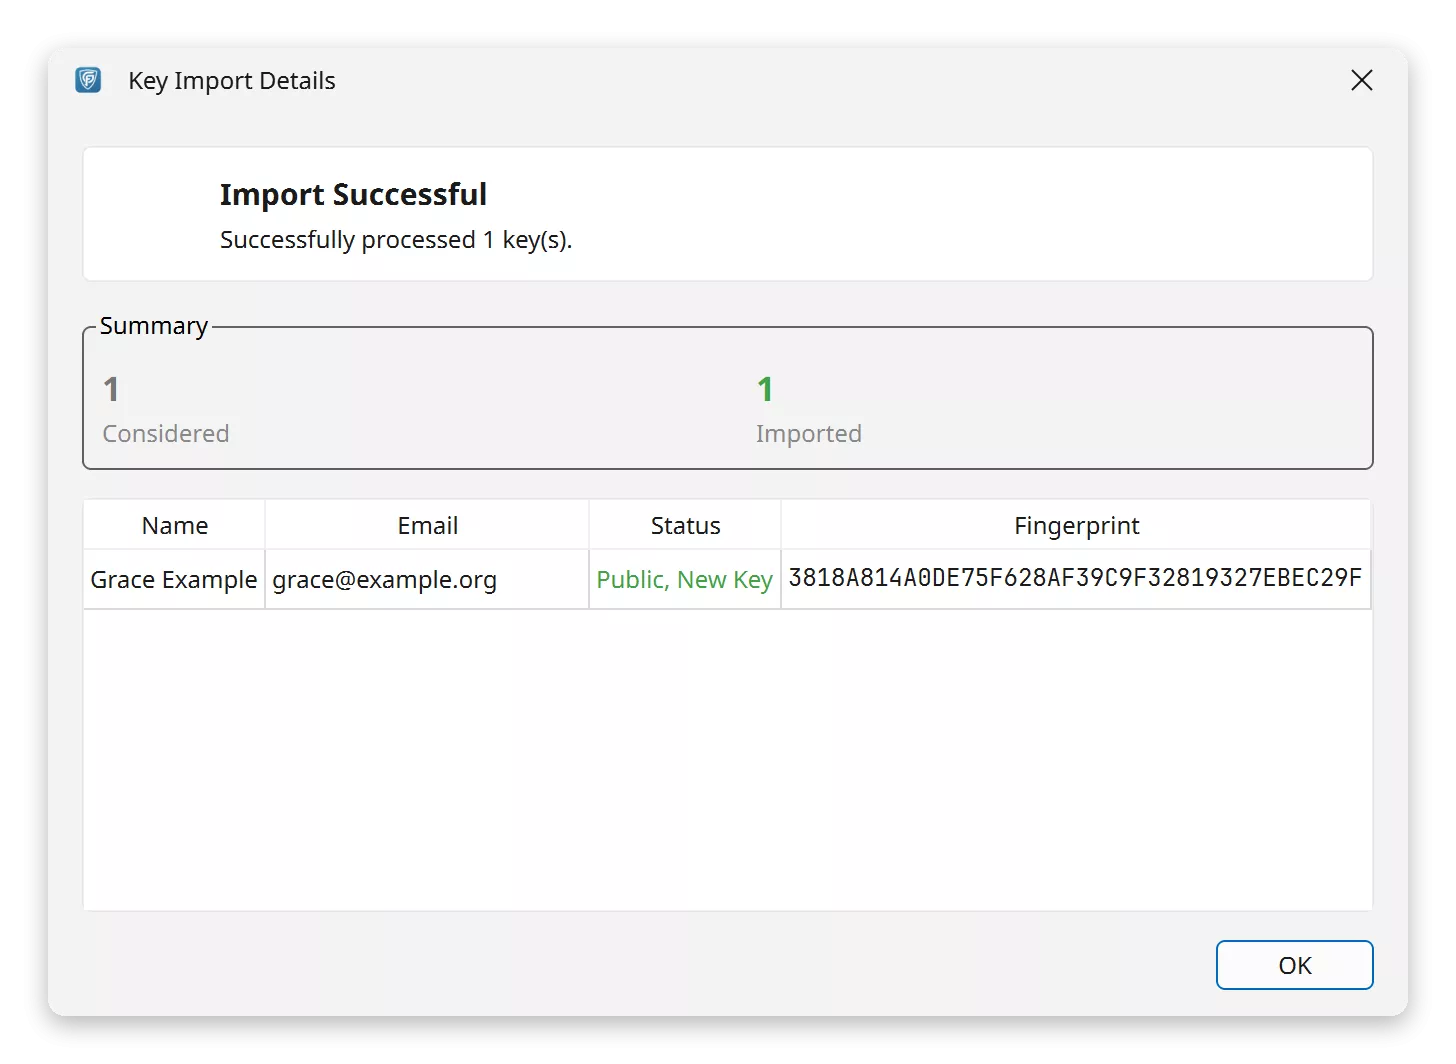
Double-click a result to import that key.
Type the full value, not a part of it:
A key ID has 8 or 16 characters.
A fingerprint has 16, 40 or 64 characters.
An email address must be complete, such as alice@example.com.
Some servers, such as keys.openpgp.org, only find a key when you type the
exact email address or the full fingerprint.
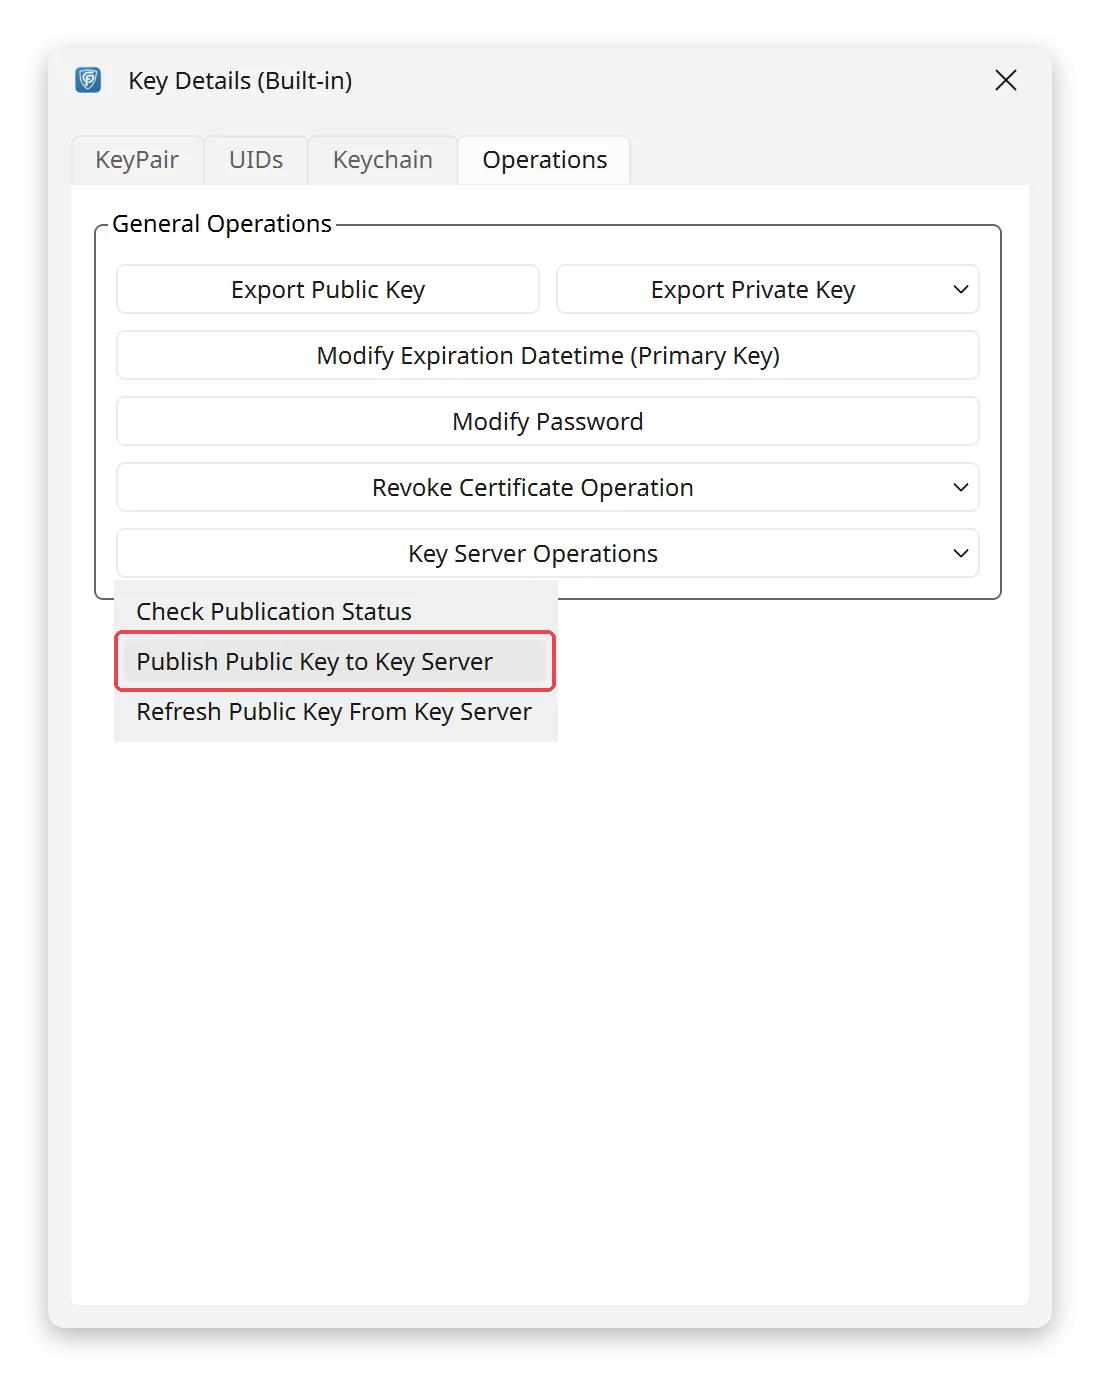
Publishing lets other people find your public key.
Only your public key is uploaded. Your private key is never sent.
Once a key is on a key server, it can spread to other servers. It may be
impossible to remove it.
Key servers accept keys in one of two ways. They are called VKS and
HKP. What happens next depends on which one your default key server
supports:
VKS
The newer way. The server checks that each email address on the key is
really yours. keys.openpgp.org works like this. GpgFrontend uploads the
key and shows each email address with its status. The server then sends
you an email. Click the link in that email. If you do not, other people
cannot find your key by its email address.
HKP
The older way. The server does not check your email address, and the
upload cannot be undone. So GpgFrontend first asks Publish Without
Verification? Click OK only if you are sure.
Refreshing downloads the newest copy of a key and adds it to your keys. Use it
to see if someone has changed or revoked their key. It works for any key,
including your own.
If the server does not have the key, the message says “The key server does not
have this key.”
Click Check Publication Status. A Publication Status message tells you
one of these:
the key is published on the server;
the key is not published on the server;
GpgFrontend could not ask the server, with the reason.
GpgFrontend never checks this by itself. Each check tells the server which key
you are interested in. So GpgFrontend only asks the server when you click.
You can publish or refresh many keys in one go. A set of keys handled together
like this is called a batch.
In a key list, tick the box next to each key you want. If you tick nothing,
GpgFrontend uses the keys you selected (clicked) instead.
Choose one of these:
Right-click the keys, then choose Publish Public Key to Key Server or
Refresh Public Key From Key Server.
In the KeyPair Management window, open the Operations menu and
choose one of the same two items.
These items are greyed out when your choice includes a key group. A key group is
not a key, so a key server cannot hold it.
When the work is done, a Key Publishing Finished or Key Refresh
Finished message sums it up. For example: “3 of 4 keys were published to the
key server keys.openpgp.org.” If some keys did not work, a Failed: list
follows, with one line for each of them.
Good to know:
Only one batch runs at a time. If you start another, GpgFrontend says “A key
server operation is already running. Try again when it has finished.”
If your key databases change while a batch runs, the batch stops. A Key
Refresh Stopped or Key Publishing Stopped message appears. None of the
fetched keys are imported. Start the batch again.
GpgFrontend waits up to 15 seconds for each answer from the server.
Type the address in the box under Add a Key Server, for example
https://keys.example.org.
Click Add.
GpgFrontend tests the new server right away. If the server does not answer like
a key server, GpgFrontend still adds it, marks it Unverified, and tells you.
If the address starts with http:// instead of https://, GpgFrontend warns
you first. With http://, anyone on the network could see and change what you
send.
The default server matters. Publishing, refreshing and Check Publication
Status always use it. They use VKS when the server offers it, and HKP
otherwise. (See Publish Your Key for what these two
mean.) If a tested server has no VKS, GpgFrontend warns you with No Verified
Publishing before it makes the change.
Searching is different. It uses HKP, and you can pick any server from the list
in the search window.
All of these features come from the KeyServerSync module, which ships with
GpgFrontend. If you cannot find Key Server in the Import Key menu, or
the Key Servers settings page, the module is turned off. See
Module Controller.