
KeyPackage file (.gfpack)
Holds your keys, encrypted.
A KeyPackage is an encrypted file that holds a set of your OpenPGP keys. Use it to move your keys safely from one computer to another, for example when you set up a new machine or want the same identity on a second device.
When you create a KeyPackage, GpgFrontend produces two files, and you set one PIN. You need all three to import the keys later:
KeyPackage file (.gfpack)
Holds your keys, encrypted.
Key file (.key)
Holds the encryption key for the KeyPackage, itself protected by your PIN. It is saved next to the KeyPackage file, unless you choose another place, such as a separate drive.
PIN
You choose it during creation. Without it, the KeyPackage cannot be opened.
Keep this in mind before you start: if you lose any one of the three, the
KeyPackage is useless. That is by design. Someone who steals just the
.gfpack file, or even both files but not the PIN, cannot read your keys.
A window called Export As Key Package walks you through three steps: Contents, Location and Protection. Click Continue to go to the next step, or Back to change something.
In the main window, click Manage Keys to open the KeyPair Management window. Check the box next to each key you want to pack, then click Export Key.
Choose Export As Key Package. The Export As Key Package window opens.
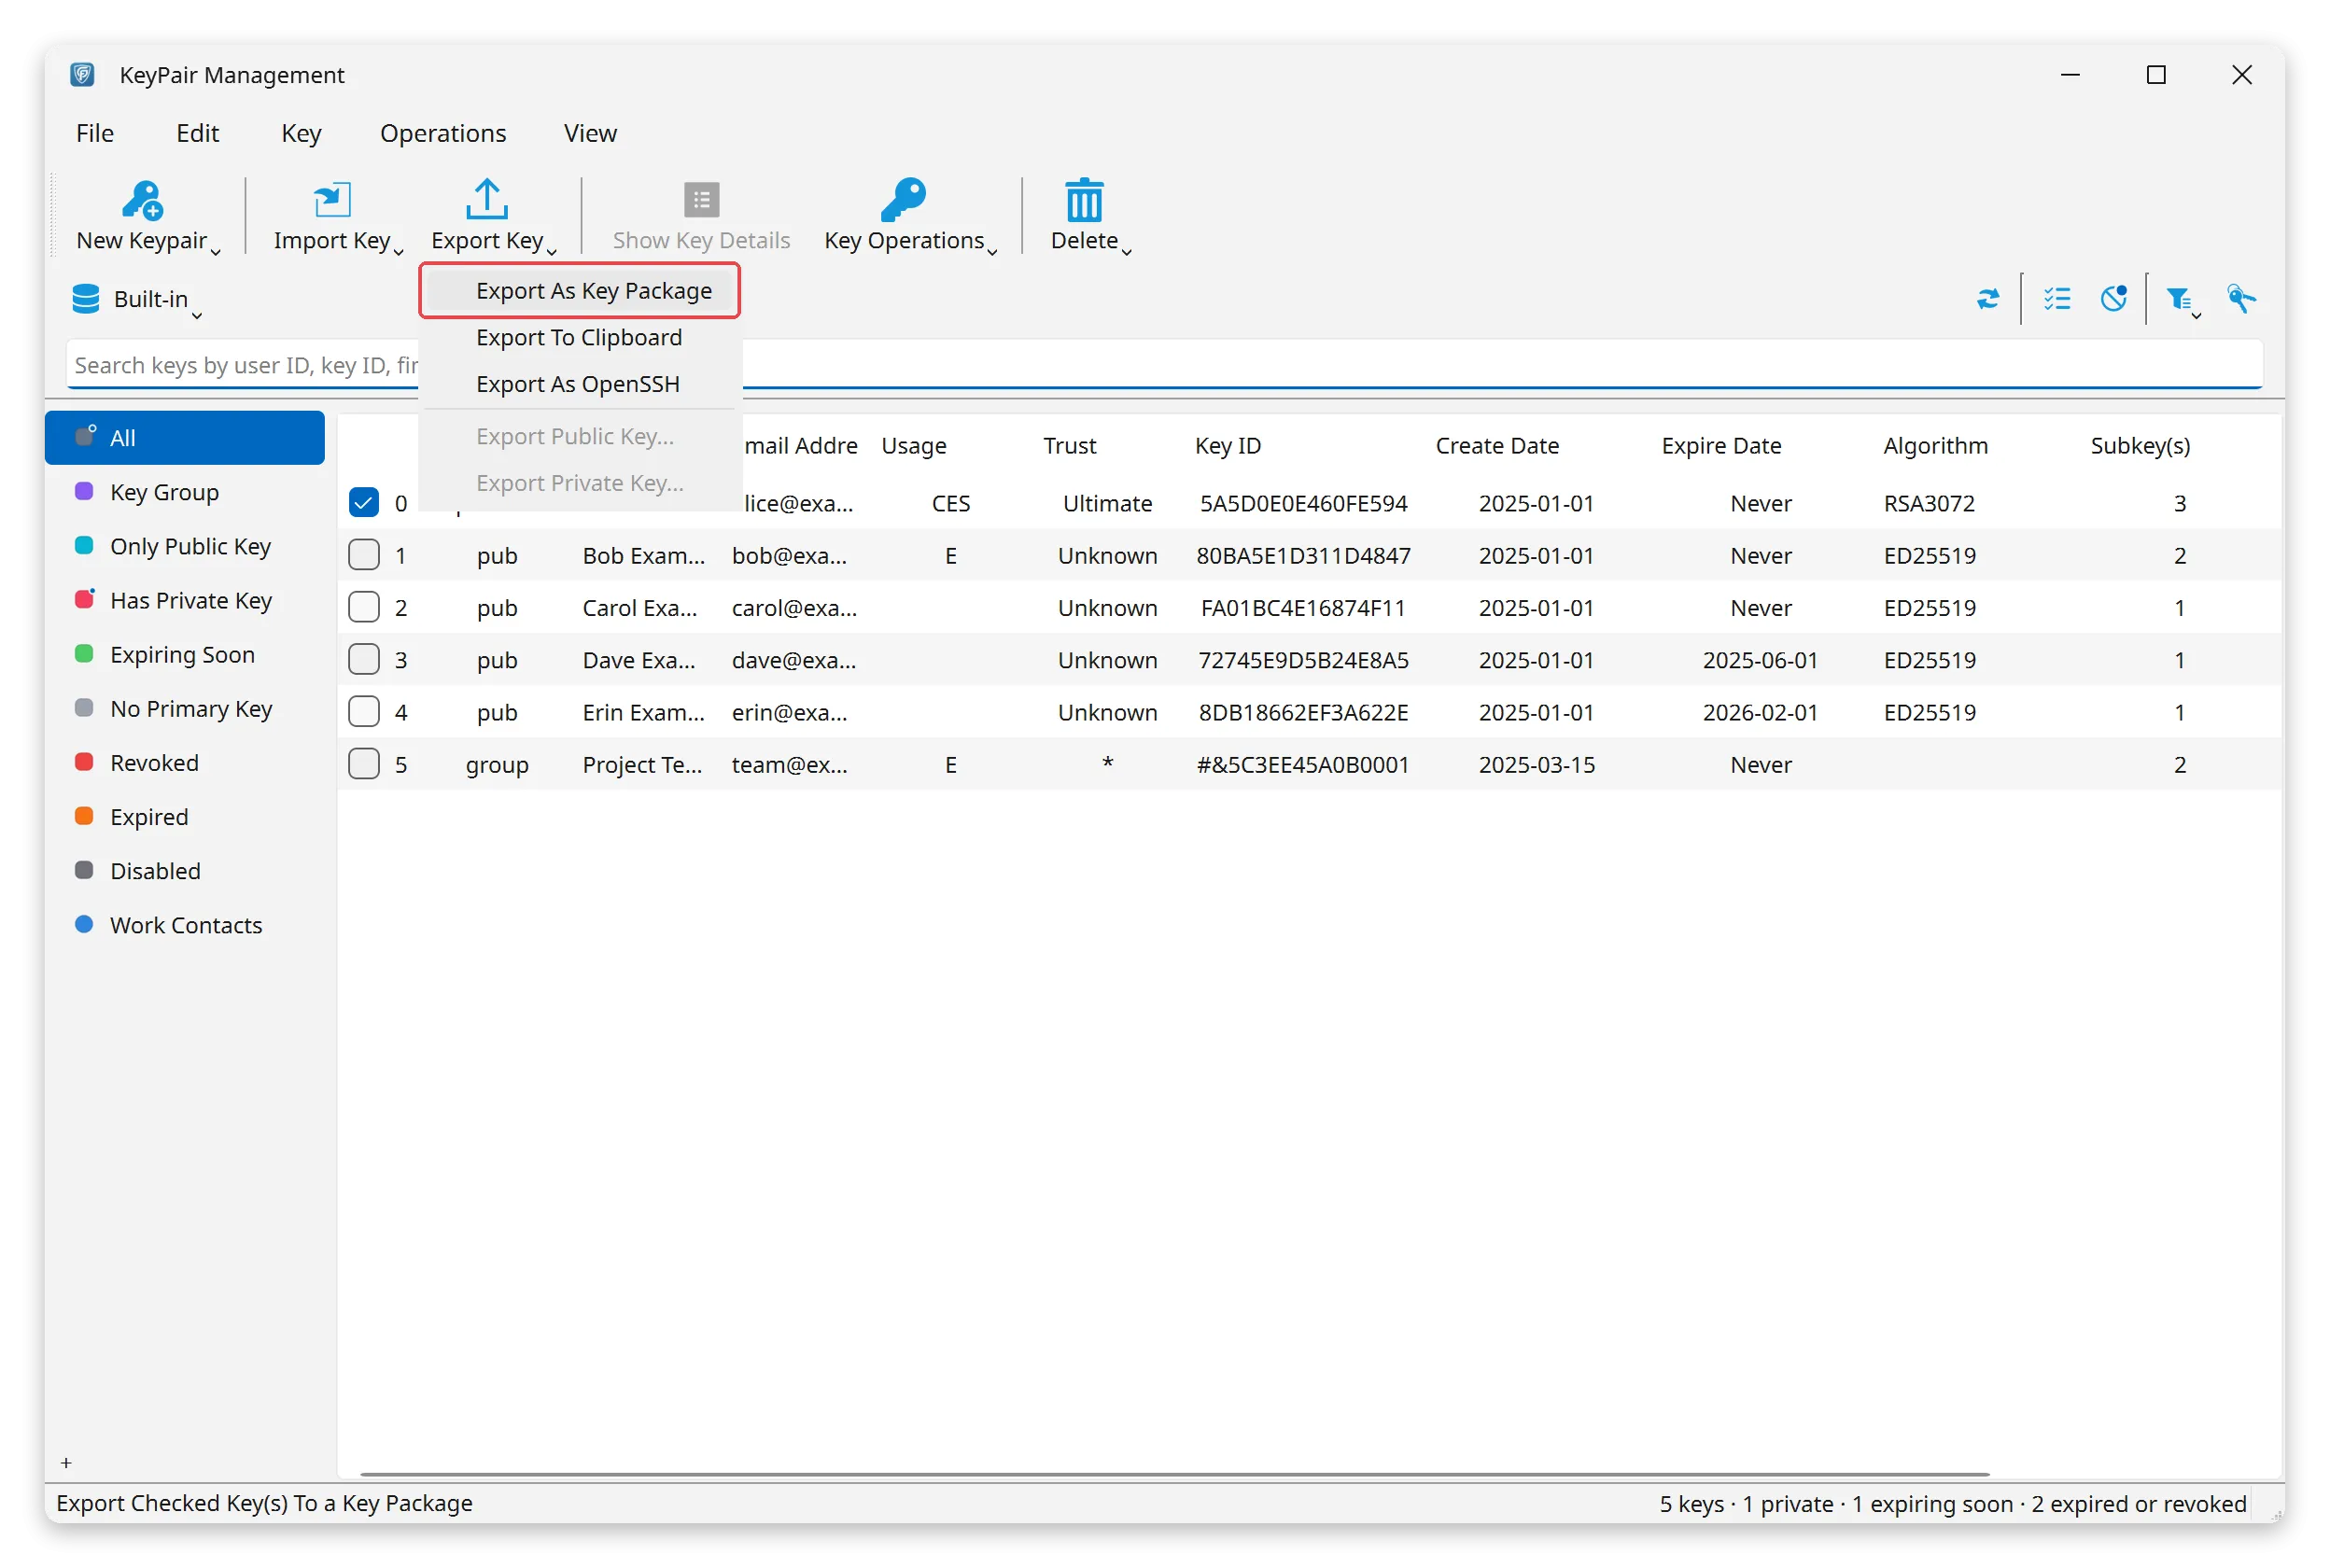
Contents: check which keys go in. A table lists each key and, in the Exported column, whether it goes in as Public, Public and private, or is Left out: no private key. Two boxes change this:
Click Continue.
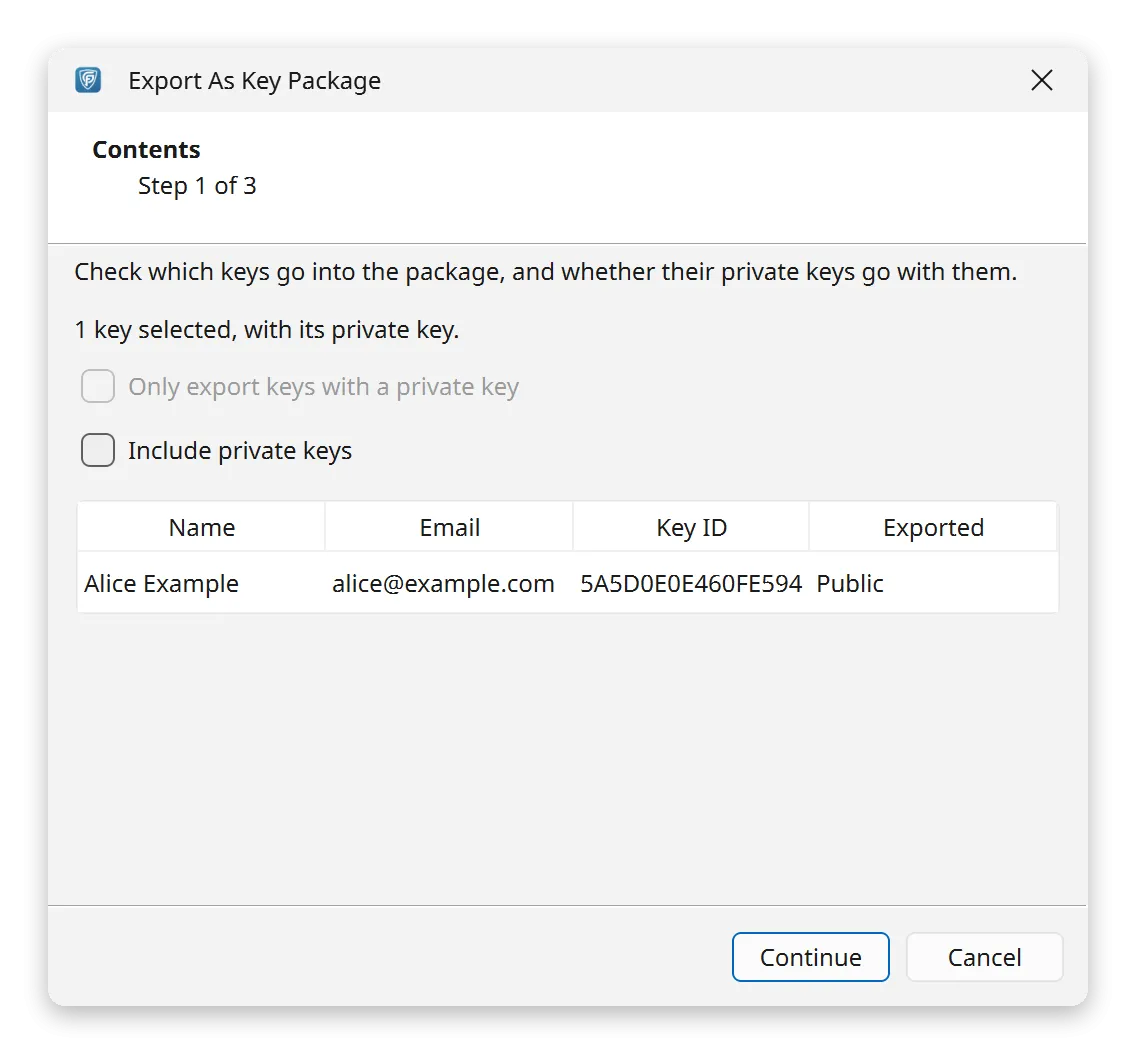
Location: choose where to save the files.
KeyPackage_<random id>. Click Generate name for a different one..gfpack
file.Click Continue.
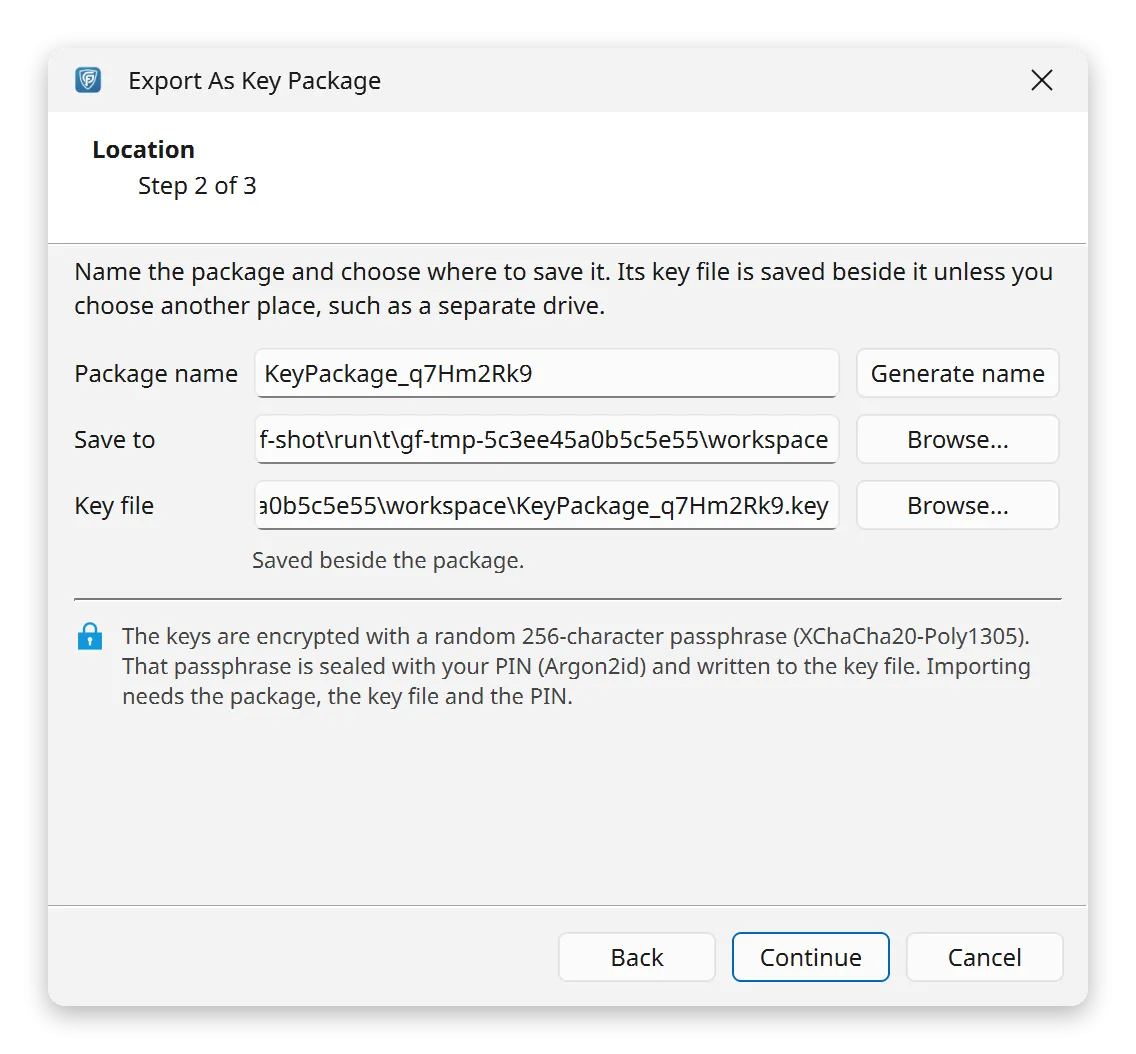
Protection: type a PIN of at least 8 characters, and type it again under Repeat. Or click Generate a strong PIN. Pick a strong one and keep it to yourself. The PIN cannot be recovered.
Check the summary of what you chose, then click Export key package.
The Key Package Exported window shows where both files were saved. Click Show in Folder to see them, or Done to close it.
To back up every private key at once, open Operations > Bulk in the KeyPair Management window and choose Back Up All Private Keys…. The same window opens, with all your private keys already included.
Move both files, the .gfpack file and the .key file, to the target
device. Use a safe method, such as an encrypted USB drive, encrypted email, or
a secure network channel.
Do not send the PIN through the same channel as the files. For example, if you email the files, tell the PIN in person or over a phone call.
On the target device:
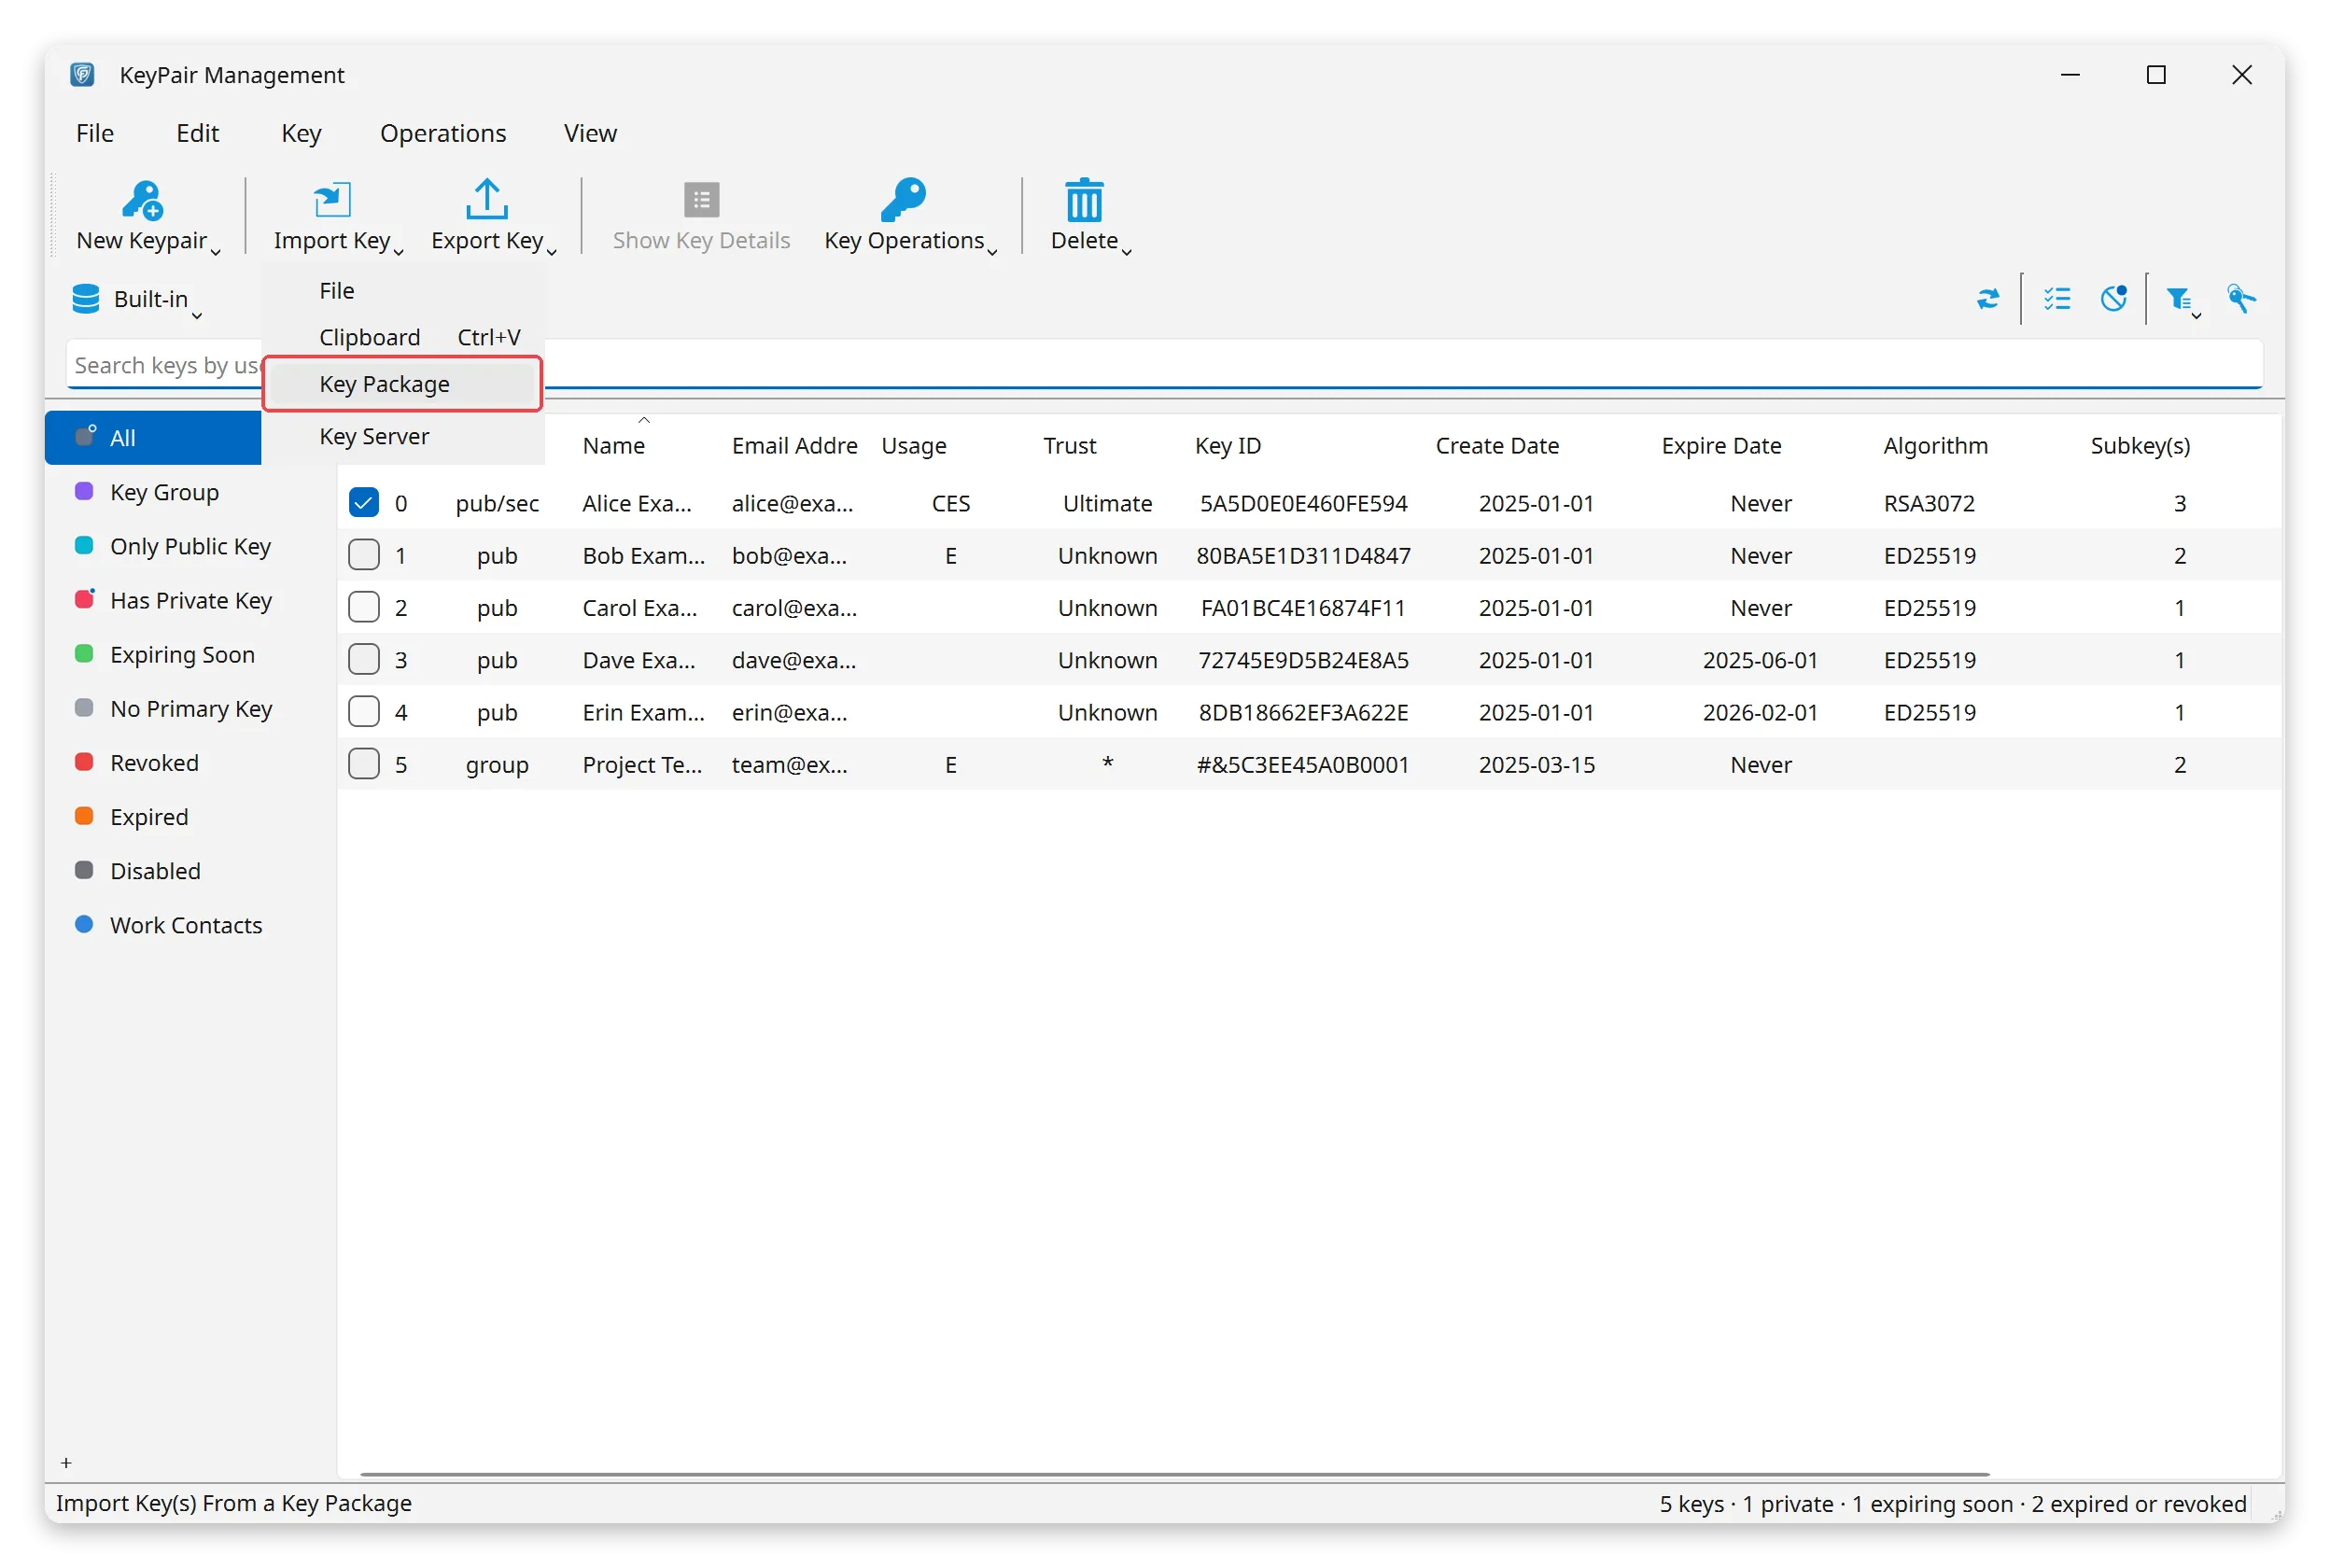
Open the KeyPair Management window and click Import Key.
From the dropdown menu, select Key Package. The Import Key Package window opens. It walks you through three steps: Files, Unlock and Keys.
Files: next to Key package, click Browse… and choose the
.gfpack file you transferred.
If the key file is in the same folder, GpgFrontend finds it by itself and
says Found beside the package. If not, click Browse… next to
Key file and choose the matching .key file. Click Continue.
Unlock: enter the PIN you set when you created the KeyPackage, then click Continue. This only opens the package. Nothing is imported yet.
If the PIN is wrong, the window says so and you can try again. Your chosen files are kept.
Keys: a table lists the keys in the package. The Status column says what importing each key would do:
Untick any key you do not want. Select all and Select none help with long lists.
Click Import keys. The window closes and Key Import Details shows what was imported.
Once the keys are imported and working:
.gfpack file and the .key file from all devices and
from any place they passed through (USB drives, email attachments, cloud
folders, download folders).The KeyPackage format has changed between GpgFrontend versions. Create and import KeyPackages with the same major version of GpgFrontend whenever possible.
You do not need this section to use the feature. It explains how the protection has improved over time:
KeyPackage_<zbase32 id>) instead of a short number.Today the keys are encrypted with a random passphrase, 256 characters long, using XChaCha20-Poly1305 (a modern way to lock data that also detects tampering). That passphrase is then locked with your PIN, using Argon2id (a method that makes guessing the PIN slow), and written to the key file.
So the PIN does not encrypt the KeyPackage directly. It protects the key file, which in turn holds the actual encryption key. This is why the import needs both files and the PIN.